Security & Infrastructure
Your business information deserves serious protection.
Security is built into the architecture from the first plan, not bolted on at the end. Here is how we protect your information, starting with what you can verify on this website right now.
01In place today
In place on this website today
A small, verifiable example of how we work: the controls protecting the inquiries you send us through this site.
- In place today
Encrypted connections
Every page is served over HTTPS, and the plain-HTTP address redirects to it.
- In place today
Browser security headers
Pages can’t be framed by other sites, file types can’t be misread, and camera, microphone and location access are switched off.
- In place today
Insert-only lead database
Database rules let the website add a new inquiry but not read existing ones. Leads are only visible in the database account itself.
- In place today
Secrets kept out of the code
The key that sends email is stored in the hosting provider’s protected settings, not in the website’s code.
- In place today
No single point of failure for inquiries
Each inquiry is saved to the database, kept in a form backup and sent by email, so one failed service doesn’t lose it.
- In place today
Analytics on the live site only
Visitor analytics run only on wit-solutions.io. Preview copies send nothing. Details are in our privacy notice.
02See it working
Watch the controls do their job.
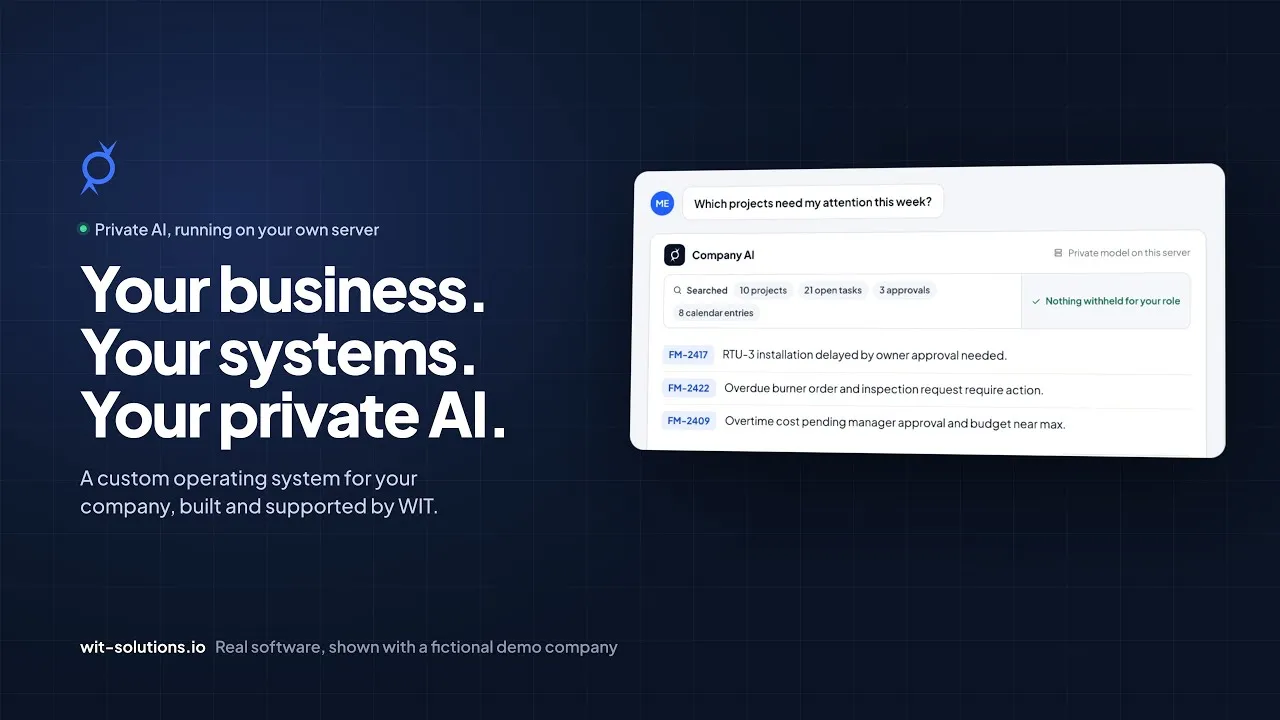
In our Command Center demo, a technician asks the company AI about profit margins. The request is blocked, and the attempt is recorded in an activity log that can’t be edited. The owner, asking about projects, gets answers only from the records they’re allowed to see.
- Role-based permissions that apply to the AI too
- Blocked attempts recorded in a log that can’t be edited
- Company AI running on the company’s own server
- Nothing happens until a person approves
03Built for your project
What we design into client systems
Each item below is part of our implementation framework. Which controls a system needs, and how far each goes, is agreed in writing during design and depends on your data, users, budget and any regulatory requirements.
- Security architectureBuilt for your projectWhere each component runs, how they connect, and which parts are reachable from the internet. Designed before anything is built.
- Authentication & MFABuilt for your projectIndividual accounts for every user, multi-factor authentication, and single sign-on with your existing accounts where supported.
- Role-based permissionsBuilt for your projectEach role sees and changes only what it needs. Access is granted and removed in one place.
- Data encryptionBuilt for your projectEncryption in transit and at rest, using the protections built into the hosting and database services we select.
- Access logging & audit trailsBuilt for your projectRecords of sign-ins and important changes, kept for the period you need.
- Secure developmentBuilt for your projectCode review, separate test and live environments, no real secrets in code, and dependencies kept up to date.
- Vulnerability managementBuilt for your projectUpdates and security patches applied on a schedule agreed in your support plan, with monitoring for known issues.
- Backups & recoveryBuilt for your projectScheduled backups, stored separately, with a restore process that is actually tested.
- AI information access controlsBuilt for your projectAI only reaches the sources you approve and filters every answer by the asking person’s permissions.
- Hosting optionsBuilt for your projectManaged cloud, dedicated hosting, an account your company owns, or on-premises where feasible.
- Business continuityBuilt for your projectA plan for outages: what keeps working, how quickly service is restored, and who is contacted.
- Incident response responsibilitiesBuilt for your projectWho does what if something goes wrong: you, WIT, and each hosting or software provider. Written down before launch.
- Software & data ownershipBuilt for your projectYour data stays yours. Ownership of the custom work is defined in your agreement, and third-party licenses are listed.
04Responsibilities
Security is shared. Here is who does what.
Clear lines of responsibility are part of good security. They’re written into your agreement before launch, including who acts first if something goes wrong.
WIT Solutions
- Designs the architecture and controls agreed in your proposal
- Builds and configures them, and documents the result
- Maintains, patches and monitors under your support agreement
Your company
- Decides who gets access and approves changes to roles
- Makes sure staff use their own accounts and MFA
- Tells us promptly when people join, leave or change roles
Hosting & software providers
- Secure their own data centers and services
- Operate under the terms of your account with them
- Are listed in your proposal, with what each one holds
05Regulated industries
Compliance, done properly
Compliance isn’t a badge you buy. It comes from how the whole system is designed, configured and operated, backed by written policies, signed agreements and independent verification.
- Regulated data, such as patient health information, payment cards or controlled technical data, is identified during scoping and designed for explicitly
- We work alongside your compliance advisors, auditors and insurer, and give them the documentation they need
- Your IT team gets a full picture: architecture, access model, backups and every provider involved
Security questions
Ask us anything else on your audit call. Your IT team is welcome to join.
Read our privacy noticeWhere will our data be stored?
In the hosting option chosen for your project: a managed cloud service, dedicated hosting, an account your company owns, or your own servers where feasible. Your proposal lists where each kind of data is stored and which providers are involved.
Can our IT team or insurer review the design?
Yes. For client systems we document the architecture, access model, backup approach and providers involved, and we’re happy to walk your IT team, insurer or advisors through it.
What happens if someone leaves the company?
With individual accounts and role-based permissions, access is removed in one place. We design that step into your offboarding process.
Is the chat assistant on this website an AI?
No. It is a scripted helper that runs in your browser. What you type into it is not sent to us or to any AI provider. To reach a person, use the contact form, call us, or book an audit.
Protect what your business runs on.
Book a free Business Operations Audit. We’ll talk through where your information lives, who can reach it, and what a secure, well-run setup would look like for your company.
- Call us(740) 602-6411
- Based inColumbus & Dayton, Ohio
- Business Operations AuditFree · 60 minutes · remote